Cyber resilience in Australia has largely been talked about in terms of networks, servers and email gateways, the territory the Essential Eight was built to defend, and APRA’s prudential standards were written to govern. That’s starting to shift. A parallel conversation about resilience is now unfolding around something more personal: the identity people carry in their pocket, and the mobile apps that verify who they are.
The clearest sign of that shift is what’s about to happen with Australia’s national Digital ID system. From 30 November 2026, private sector organisations become eligible to apply to join the Australian Government Digital ID System (AGDIS) for the first time [1][2]. Banks, insurers, telecommunications providers and other regulated entities will be able to build identity verification flows on top of a federally accredited system rather than their own bespoke onboarding processes. For CISOs, compliance leads and technology decision-makers, that’s a near-term integration decision — and one that lands squarely inside two frameworks many of these organisations already live under: the Essential Eight and APRA’s prudential standards.
Why Cyber Resilience Now Runs Through Digital Identity
Digital ID uptake in Australia has moved fast. As of December 2025, more than 15 million Australians held a myID, and verified transactions through AGDIS had more than tripled year-on-year to reach 80 million [2]. Trust hasn’t kept pace with adoption, though: auDA’s most recent Digital Lives of Australians research found that 71% of Australians who don’t hold a Digital ID cite security worries as the reason [3]. That’s the gap cyber resilience frameworks exist to close, and it’s a gap that now sits on the device layer as much as the network layer.
When the primary access channel for a national identity system is a smartphone, the attack surface for identity fraud shifts with it, from forged paperwork to compromised endpoints, cloned applications, and credentials lifted through malware or overlay attacks rather than stolen wallets. The Essential Eight wasn’t written with Digital ID in mind, but the underlying problem it targets, hardening the endpoints and applications that hold sensitive access, is precisely the problem digital identity now runs on top of.
Essential Eight: The Baseline Behind the Headlines
The Essential Eight remains, at its core, eight prioritised mitigation strategies mapped against four maturity levels, first published by the Australian Signals Directorate in 2017 and updated regularly since [4]. It isn’t a certification, and outside non-corporate Commonwealth entities it isn’t universally mandated, but it has become a default reference point in tenders, contracts and cyber insurance assessments.
What’s Changed Heading Into 2026
Two shifts matter for anyone revisiting their posture this year. First, ASD has lowered the bar at which phishing-resistant MFA is required: it now applies from Maturity Level Two rather than only at the top level, and a new requirement covers phishing-resistant authentication to workstations themselves, a direct response to the rise of real-time phishing and credential-based attacks [5]. Second, ASD’s own assessment guidance now grades evidence quality explicitly, and rates a verbal or policy statement of intent as the lowest tier of evidence available; “we patch within 48 hours” needs a demonstrable audit trail behind it, not an assertion [6].
Where Mobile Identity Intersects With Essential Eight
None of the Essential Eight’s strategies were written as a mobile app security specification, and no technology genuinely makes an organisation “Essential Eight compliant.” But the intent behind several of them, verified access, controlled and patched applications, hardened endpoints, maps directly onto how a digital identity credential is protected once it’s sitting inside a mobile app on a personal device. An organisation can have exemplary MFA policy on paper and still have it undermined at runtime if the app carrying the credential can be tampered with, run undetected on a compromised device, or have its communications intercepted.
APRA’s Expectations: CPS 234, CPS 230 and Digital Identity
For APRA-regulated entities, banks, insurers and superannuation trustees, the relevant obligations sit in two connected prudential standards. CPS 234 (Information Security) requires information security capability commensurate with the threat exposure of an entity’s information assets, holds the board ultimately accountable, and requires APRA to be notified of material information security incidents within 72 hours [7]. CPS 230 (Operational Risk Management), in force since 1 July 2025, requires entities to identify critical operations, set impact tolerances, and manage the risk posed by material service providers, including APRA’s contractual right to review documentation and conduct on-site visits [8]. Pre-existing service-provider contracts had until the earlier of their next renewal date or 1 July 2026 to be brought into line, a deadline that has now passed, meaning any digital identity provider relationship that qualifies as a material service arrangement should already meet the standard [8].
The connection to digital identity is direct: once a bank or insurer integrates with an external Digital ID provider, that relationship is very likely to meet the definition of a material service-provider arrangement under CPS 230, and the identity verification flow itself becomes an information asset inside CPS 234’s scope. Using an accredited, federally regulated identity system doesn’t discharge the entity’s own security and reporting obligations, it adds a dependency that has to be managed under the same standards as any other.
Where Australia’s Digital ID Rollout Actually Stands
The Digital ID Act 2024 came into force on 30 November 2024, establishing the Australian Competition and Consumer Commission as Digital ID Regulator overseeing accreditation, and giving the Office of the Australian Information Commissioner an expanded privacy role [1]. Amendments finalised in November 2025 strengthened the Digital ID Rules and introduced a redress framework for individuals affected by fraud or cyber security incidents within AGDIS [9]. None of that is forthcoming, it’s already operating.
What’s still ahead is the part most relevant here: private sector entities become eligible to apply to join AGDIS from 30 November 2026, whether as accredited providers or relying parties verifying customers [1][2].
The practical takeaway for a bank, telco or insurer is straightforward: within the next reporting cycle, using a federally accredited Digital ID to verify a new customer stops being theoretical and becomes an option on the table, one that sits inside the Essential Eight and APRA obligations already covered above, not outside them.
The Missing Layer: Mobile App Security as the Foundation of Digital Identity Trust
This is where the policy story, the Essential Eight conversation and the APRA obligations converge on one practical point: none of it means much if the mobile app carrying the identity credential, biometric template or authentication key isn’t itself defensible.
That’s the layer easiest to overlook, sitting below the policy debate and the compliance audit, inside code running on millions of individual devices, many rooted, jailbroken, or otherwise outside an organisation’s control. It’s also where the practical use cases for digital identity, eKYC onboarding, biometric login, one-tap authentication, actually live or die. An eKYC flow with a flawless liveness check is only as trustworthy as the app performing it; a passwordless method is only as phishing-resistant as the runtime protecting its keys.
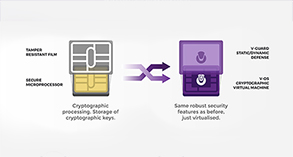
This is the specific gap that mobile app security and app-level digital identity technologies, including V-Key’s own V-OS-based approach to tamper-resistant, software-based protection, are built to address: giving mobile applications a verifiable identity of their own, and protecting the credentials inside them even when the device can’t be fully trusted. It’s a complement to Essential Eight and APRA compliance work, not a replacement for either.
Building a Digital Identity Strategy That Can Withstand Scrutiny and Attack
A few questions are worth answering before the 30 November 2026 opening, not after:
- Where do identity credentials actually live today, and how would that change once a federally accredited Digital ID provider joins the onboarding or verification flow?
- Does mobile app hardening reflect the intent of Essential Eight, verified access, controlled applications, protected endpoints, even where the framework isn’t formally mandated?
- Has any prospective Digital ID integration been assessed as a material service-provider relationship under CPS 230, with the corresponding risk register and contractual protections in place?
- Is information security capability for that integration commensurate with the threat, as CPS 234 expects, rather than assumed because the provider itself is accredited?
Essential Eight and prudential standards like CPS 234 and CPS 230 are best treated as a floor for this work, not a finish line. As Australia’s digital identity system opens to a much wider set of organisations over the next twelve months, the entities that get the most value out of it, with the least regulatory and reputational risk, will be the ones that treated mobile app security as part of the same conversation as compliance from the outset.
V-Key works with banks, telcos, government agencies and technology companies across the region on mobile app protection and digital identity infrastructure. Explore how V-Key ID and V-OS Mobile App Protection support this kind of work.
Sources & References
- Department of Finance, Digital ID Act 2024, Digital ID System — commencement date (30 November 2024), ACCC as Digital ID Regulator, OAIC’s expanded privacy role, and AGDIS expansion to the private sector no later than two years after commencement.
https://www.digitalidsystem.gov.au/what-is-digital-id/digital-id-act-2024
- Senator the Hon Katy Gallagher, Minister for Finance, “More than 15 million Australians choose simpler, safer Digital ID,” media release, 4 December 2025 — 15 million myIDs and 80 million verified AGDIS transactions (more than tripled year-on-year) as at that date; confirmation that private sector providers can apply to join AGDIS from 30 November 2026.
https://ministers.finance.gov.au/financeminister/media-release/2025/12/04/more-15-million-australians-choose-simpler-safer-digital-id
- auDA, Digital Lives of Australians 2025 (research conducted with SEC Newgate Research) — finding that 71% of Australians without a Digital ID cite security concerns as the reason, as summarised on auDA’s website.
https://www.auda.org.au/news-insights/blog/navigating-the-digital-lives-of-australians-challenges-and-solutions/
- Australian Signals Directorate / Australian Cyber Security Centre, Essential Eight Maturity Model, cyber.gov.au — framework structure (eight strategies, four maturity levels), first published June 2017 and updated regularly.
https://www.cyber.gov.au/business-government/asds-cyber-security-frameworks/essential-eight/essential-eight-maturity-model
- Australian Cyber Security Centre, Essential Eight Maturity Model Changes, cyber.gov.au — addition of phishing-resistant MFA requirements at Maturity Level Two and the new workstation-authentication requirement.
https://www.cyber.gov.au/business-government/asds-cyber-security-frameworks/essential-eight/essential-eight-maturity-model-changes
- Australian Cyber Security Centre, Essential Eight Assessment Process Guide, cyber.gov.au — defined evidence-quality tiers for assessment, with a verbal or policy statement of intent rated as the lowest (“poor”) tier of evidence.
https://www.cyber.gov.au/business-government/asds-cyber-security-frameworks/essential-eight/essential-eight-assessment-process-guide
- Australian Prudential Regulation Authority, Prudential Standard CPS 234 Information Security.
https://www.apra.gov.au/standards/cps-234
- Australian Prudential Regulation Authority, Operational Risk Management (CPS 230) — effective date (1 July 2025), material service-provider obligations, and the transitional deadline (earlier of contract renewal or 1 July 2026) for pre-existing service-provider arrangements.
https://www.apra.gov.au/operational-risk-management
- Department of Finance, “Digital ID Rules updated to better support individuals,” Digital ID System — 2025 amendments to the Digital ID Rules and the introduction of the redress framework, which commenced 19 November 2025.
https://www.digitalidsystem.gov.au/news/digital-id-rules-updated-to-better-support-individuals